ISO 27001 softwareProve your security
The ISO 27001 checklist ready to use, every policy and record in one place, and cybersecurity experts by your side. Prepare once, stay ready every year.
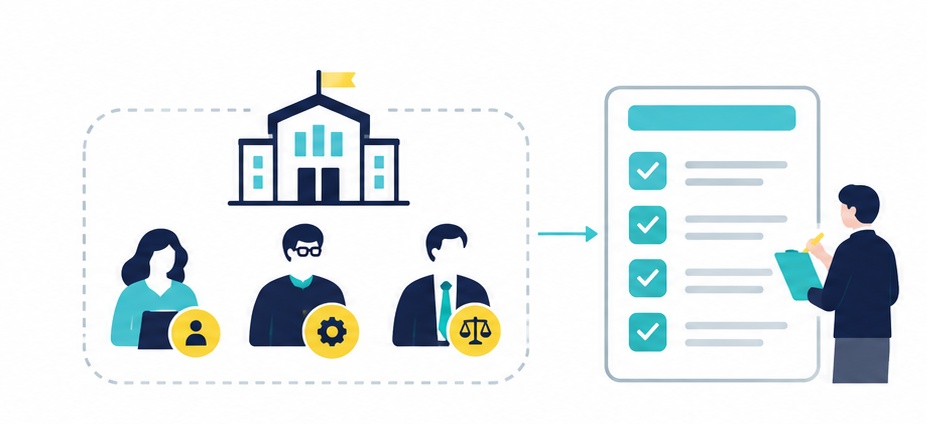
ISO 27001 isn’t only an IT project. That’s why the evidence is everywhere.
ISO 27001 covers people, processes and buildings, not only systems. The proof that your information security works sits with many people across the company.
It sits with every team
Policies with management, access reviews with IT, training records with HR, contracts with legal, supplier checks with procurement.
It lives in folders and inboxes
Risk registers in spreadsheets, policies in shared drives, evidence of controls in emails. Nobody has the full picture.
It comes back every year
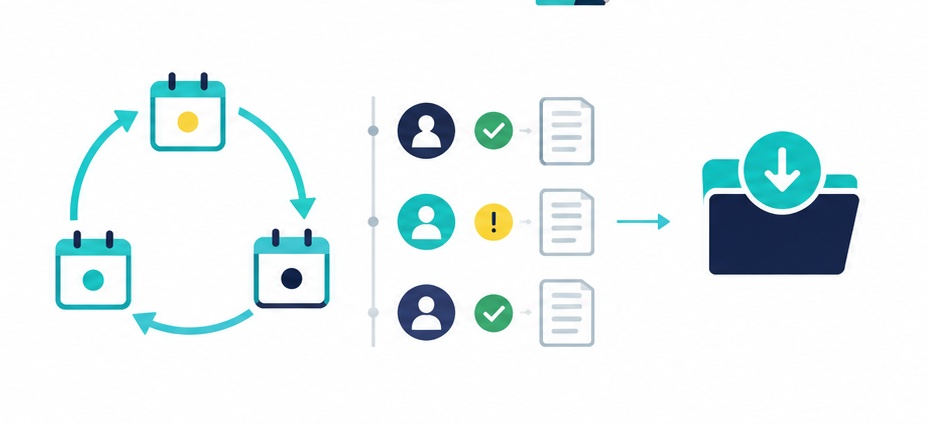
Certification runs on a three-year cycle with a surveillance audit every year. The same evidence has to be collected, updated and shown again and again.
Our ISO 27001 compliance software brings all of it into one place, organised around what the standard asks of you.
ISO 27001 compliance, without the headache
- The ISO 27001 checklist, already built.Start from a ready ISO 27001 checklist instead of a blank spreadsheet, and adapt it to your scope.
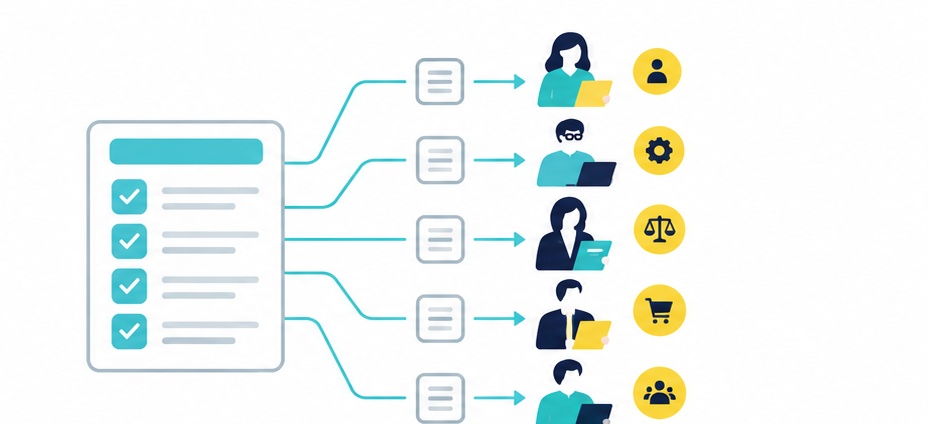
- Every requirement has an owner.Send each control and document to the person who holds it, in any team or site.
- One place for every document.Policies, risk assessments, your Statement of Applicability, training records and supplier checks, each linked to its requirement.
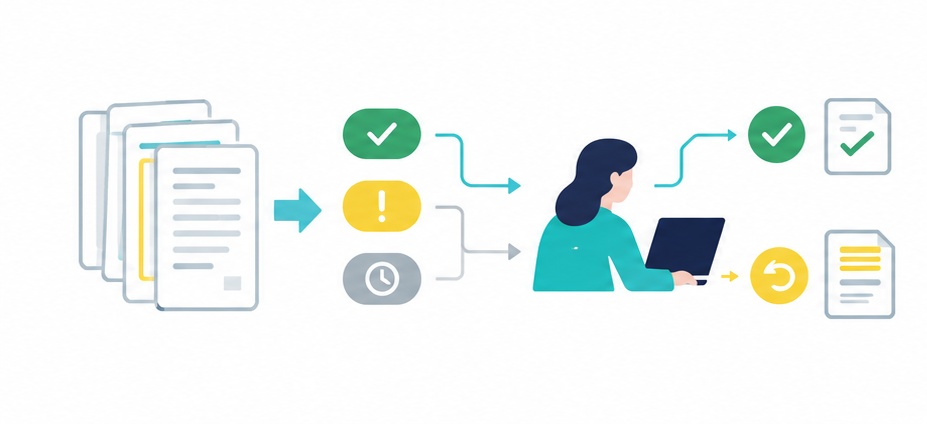
- You always know what’s missing.See at a glance what’s done, under review or still open, by team.
- Cybersecurity experts behind it.Our team helps you set your scope, assess your risks and close the gaps.
The ISO 27001 checklist: every requirement, with its evidence attached
The ISO 27001 checklist in our software follows the standard. Each requirement has its owner, its documents and its status.
Scope and leadership
What your information security management system covers, your security policy and who is responsible for what.
Risks and controls
Your risk assessment, how you treat each risk, and your Statement of Applicability: which of the standard’s controls apply to you, and why.
Proof that controls work
Records that show your controls in practice, from access reviews and training to supplier checks and incident handling.
Internal audits and management reviews
The results of your internal audits and management reviews, and what you did about the findings.
How it works
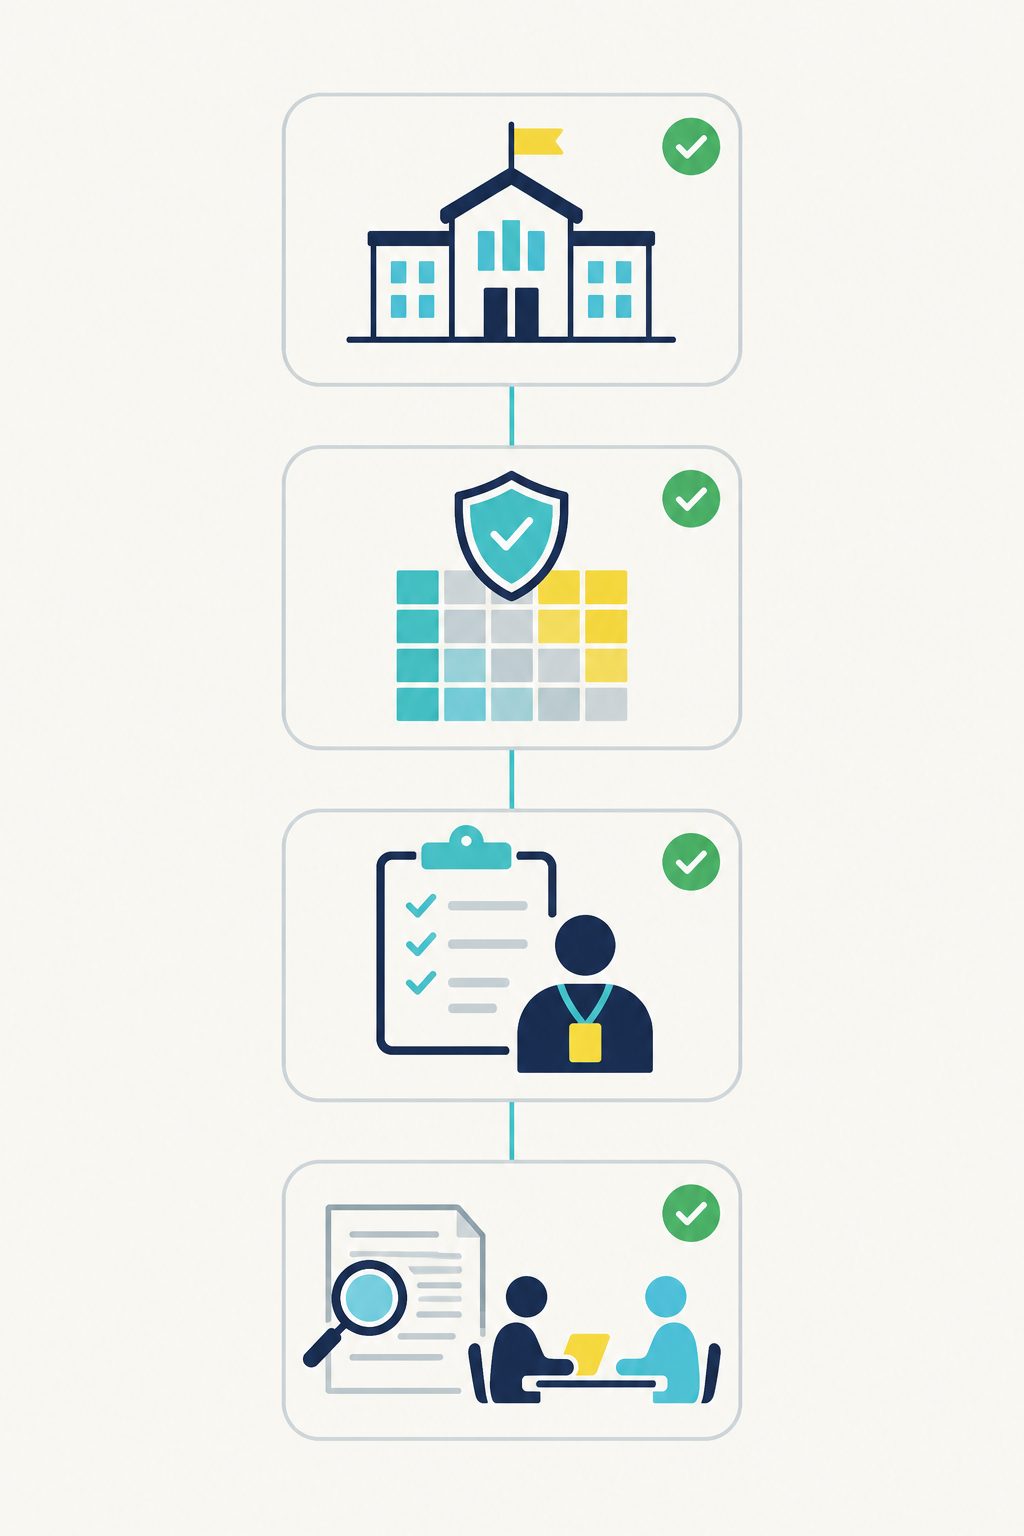
Four steps, and your ISO 27001 evidence is under control
Not just software. Cybersecurity experts by your side.
A checklist alone doesn’t make you secure. Our cybersecurity team works with you on the parts that need judgement, so ISO 27001 doesn’t take over your year.
We set your scope
Which teams, sites and systems your management system covers.
We help you assess your risks
Your risk assessment, risk treatment and Statement of Applicability.
We help you close the gaps
Policies, procedures and the evidence each control needs.
We stay with you
A yearly internal review before your surveillance audit, and support to keep improving.
Not sure where to start? Tell us about your scope and where you stand, and our cybersecurity team will show you your ISO 27001 checklist in our software.
Talk to a cybersecurity expertAlso from our cybersecurity team: penetration testing and vulnerability assessments, secure development, and incident response.
Peterson Solutions is a consultancy, not a certification body. Your accredited certification body carries out the audit independently; our support doesn’t guarantee the outcome.
Explore Peterson’s certification support →See our cybersecurity and technology services →
More than a tool: cybersecurity experts on your side
Behind our ISO 27001 compliance software there is a team that knows the standard and the software, and works with you from setup to your certification audit.
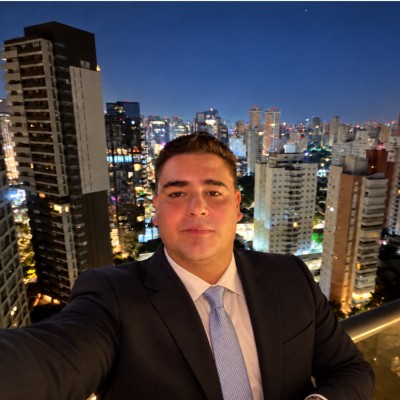
Kevin Gracia
Head of Information Security and Privacy Certification
More than ten years of experience in information security, privacy, risk and cybersecurity, including as an ISO 27001 lead auditor leading certification audits against international standards.
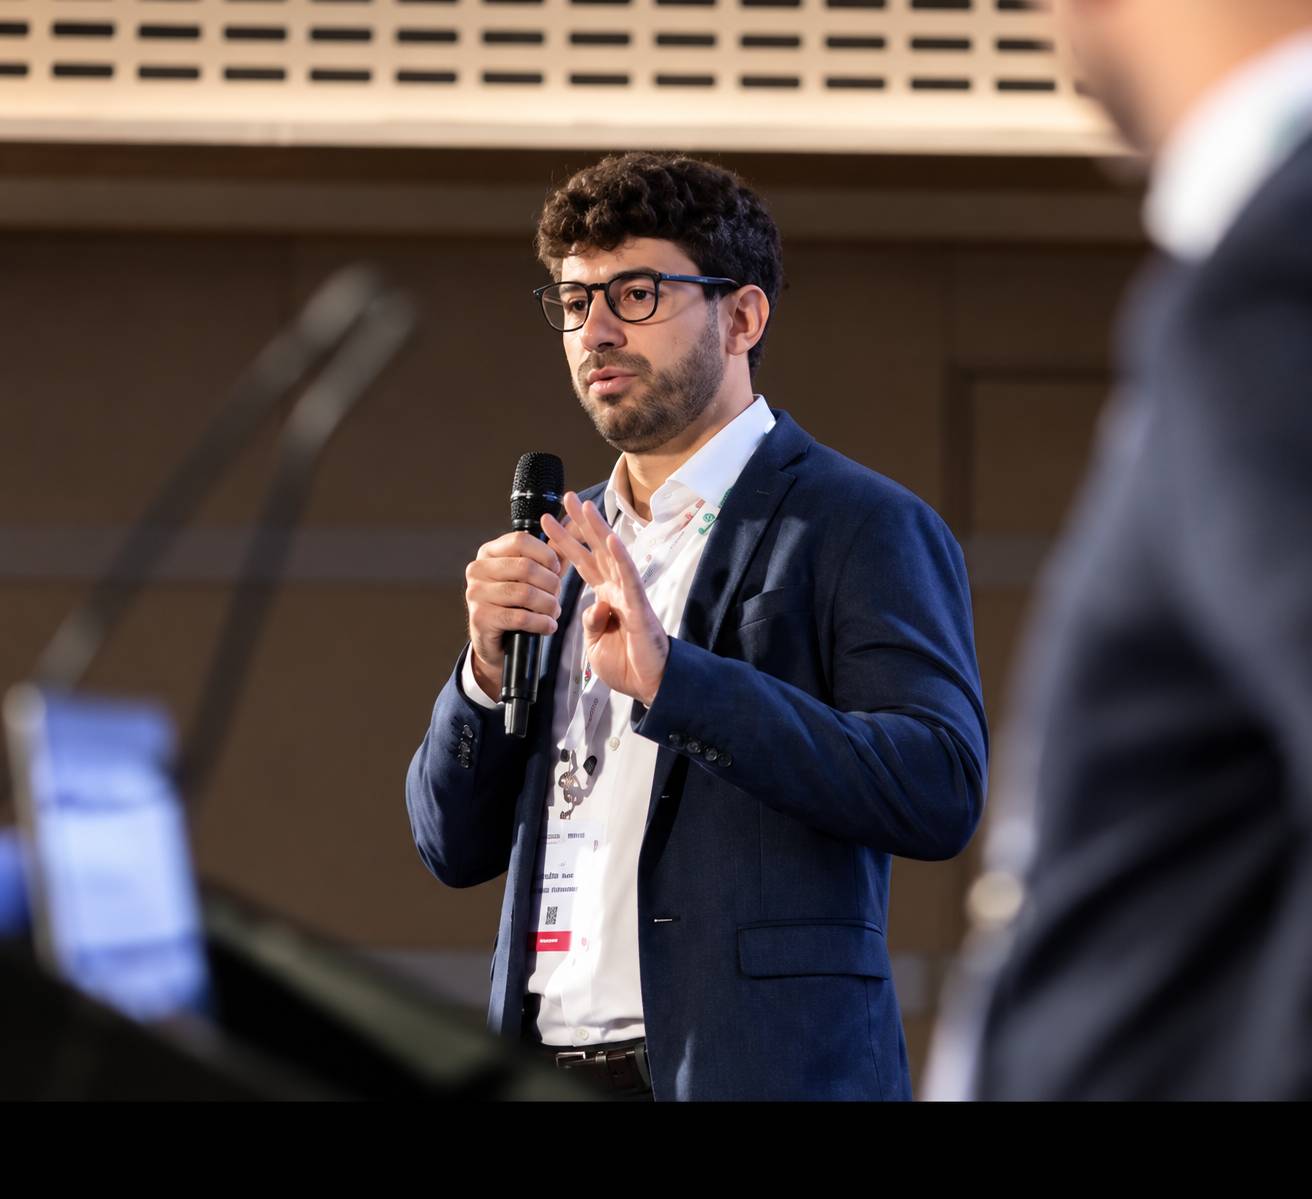
Valentin Feliu
Lead Product Manager, Peterson Technologies
Leads product work on our sustainability and compliance software from Madrid. Joined Peterson in 2024 as CSRD Lead and holds a Master in Business Analytics and Big Data.
Built for companies that are asked to prove they handle data safely
Software, SaaS and cloud companies
Asked for ISO 27001 by their clients.
IT and managed service providers
With many teams and clients to answer for.
Companies that process data for others
Such as outsourcing, payroll or payment services.
Suppliers bidding for tenders and large contracts
Public tenders or large corporate contracts that ask for ISO 27001.